How to Fix Mixed Content Warning WordPress
Remove mixed content warnings by updating insecure WordPress URLs, fixing theme assets, checking HTTPS settings, and clearing caches.
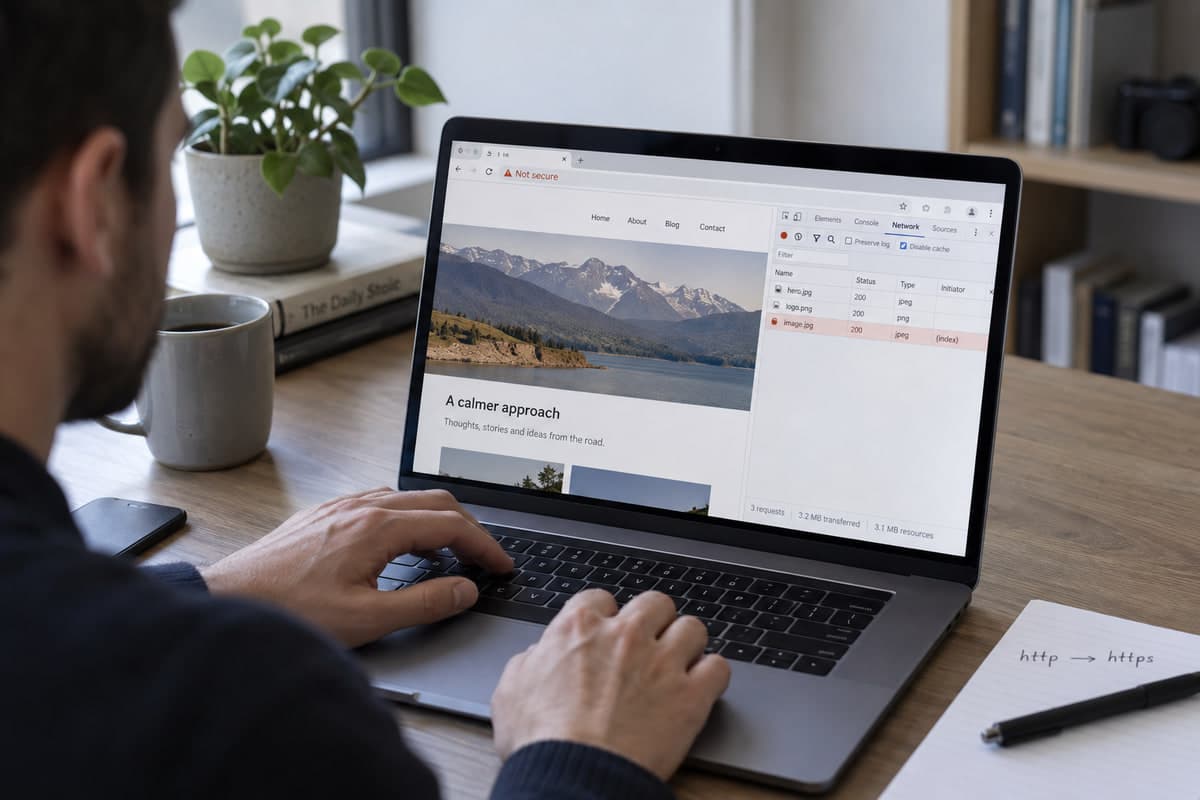
You install an SSL certificate, the website opens with https://, but the browser still shows a security warning. This often happens because the page is secure while one or more images, scripts, fonts, or stylesheets still load over http://.
That combination is called mixed content. The fix is to identify and update the insecure requests.
Confirm the Certificate and WordPress URLs
First, open the HTTPS version of your website and verify that the certificate is valid for the domain. Then go to Settings → General and confirm that both the WordPress Address and Site Address use https://.
Do not change these URLs casually on a site with an unusual subdirectory or proxy setup. A wrong value can lock you out.
WordPress is compatible with HTTPS when the server has a valid certificate, as explained in the official HTTPS administration guide.
Find the Insecure Resources
Open the affected page in your browser, launch Developer Tools, and check the Console and Network tabs. Look for resources requested through http://.
Typical sources include:
- Images inserted before HTTPS was enabled
- Theme background images
- Custom CSS font URLs
- Old JavaScript libraries
- Page-builder templates
- External embeds that do not support HTTPS
Write down the exact URLs and the pages where they appear.
Update URLs in WordPress Content
For a few pages, edit the affected image or link manually. For a large site, use a safe database search-and-replace tool or WP-CLI to replace the old HTTP domain with the HTTPS version.
Create a full database backup first. Serialized data can be damaged by a careless raw SQL replacement, so use a WordPress-aware tool and run a dry test when available.
Check Theme and Plugin Files
Hard-coded URLs may live in theme settings, Customizer fields, custom CSS, header scripts, or plugin options. Replace them with HTTPS URLs or protocol-independent WordPress functions where appropriate.
Do not edit a third-party parent theme directly. Use a child theme or the product’s supported settings so updates do not erase the change.
Review CDN and Proxy Settings
If you use a CDN, update its origin and public URL to HTTPS, then purge its cache. A reverse proxy must send the correct protocol headers so WordPress recognizes secure requests.
Avoid “flexible” SSL arrangements that encrypt only the visitor-to-CDN connection while leaving the origin misconfigured. Use end-to-end HTTPS when your provider supports it.
Clear Caches and Retest
Purge WordPress, server, CDN, and browser caches. Test several templates: homepage, posts, archives, forms, login, and checkout.
If the warning remains, repeat the browser-console check. A single old font or background image can affect every page.
Add Redirects After HTTPS Works
Once all resources load securely, add a redirect so http:// visitors land on https://. Keep this rule in one layer only—WordPress, the server, or the CDN. Not all three. Multiple HTTPS redirects cause the "too many redirects" error.
Conclusion
Mixed content is usually leftover content rather than a broken certificate. Find every insecure request, update it at the source, clear all caches, and only then enforce the final HTTPS redirect.
Share